
Authorities say a teenage suspect may have been at the center of a ransomware operation that stretched across continents, hit hundreds of victims, and pulled in stolen data on a massive scale. The case has now become a sharp reminder that cybercrime is no longer just the work of hardened adults in dark rooms, and that the pressure tactics behind ransomware keep evolving fast.
Investigators linked the KillSec operation to roughly 1,000 suspected attacks worldwide, with about 500 confirmed as successful so far. International police shut down key servers and seized the group’s leak site, along with 110 terabytes of stolen data that could have been used to shame victims, extort money, or spread sensitive records far and wide.
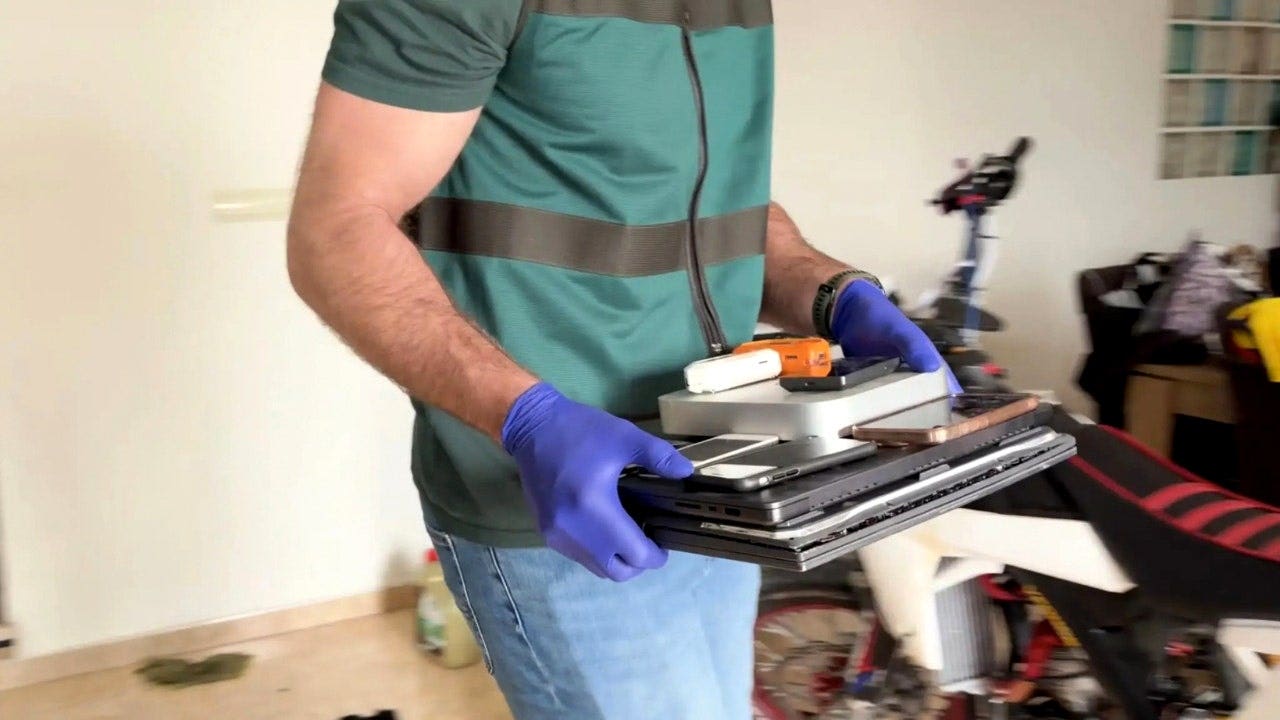
The crackdown, known as Operation KillSwitch, brought together agencies from the United States and several European countries. Police carried out searches in Greece, Romania, Spain and the United Kingdom, and three suspects were provisionally arrested as the investigation widened. Officials also took control of five central servers tied to the group’s operation, cutting off a major chunk of its online reach.
What makes the case stand out is the age of the alleged main operator. Investigators say a 16-year-old was the suspected administrator and primary driver behind the group, while another suspected member was still a minor when some of the crimes were said to have happened. That detail has grabbed attention, but the bigger story is how accessible the tools of cybercrime have become.
KillSec allegedly leaned on a familiar ransomware playbook. According to investigators, the group exploited software flaws and weak access controls to break into organizations, then copied internal files to systems they controlled. Once the stolen data was in hand, the group reportedly used it as leverage, threatening to publish records unless victims paid up.
That kind of pressure has become the backbone of modern ransomware. Criminals do not always need to lock every file to cause damage, because stolen customer information, employee records, and business documents can be just as painful to expose. Even when backups are intact, the threat of public leaks can still force companies into a corner.
Another detail that raised eyebrows was the reported use of artificial intelligence. Europol says members of KillSec used AI to help build and maintain parts of the ransomware infrastructure and to identify possible targets. AI did not run the attacks on its own, but it appears to have made certain jobs faster, easier, and less technical for the people behind them.
That matters because it lowers the barrier to entry. A would-be hacker no longer needs to be a genius coder to get started if stolen credentials, weak systems, and automated tools can do some of the heavy lifting. The mix of basic mistakes and newer technology is exactly what makes these attacks so hard to ignore.
Even though KillSec focused on organizations, the lessons reach far beyond the corporate world. Old routers, forgotten accounts, reused passwords, and unpatched devices are still the kind of openings attackers love to find. One weak spot can be enough to let criminals inside before anyone notices the first sign of trouble.
That is why the basics still matter so much. Keeping software updated closes off known flaws, while unique passwords and two-factor authentication make stolen credentials less useful. Backups also matter, especially if one copy is kept offline so ransomware cannot reach it once an infection starts spreading.
People also need to stay sharp about phishing emails, fake update alerts, and suspicious attachments. A single careless click can hand over access faster than most people realize. Security software can help catch some threats early, but it works best when paired with habits that make it harder for criminals to get a foothold in the first place.
The KillSec takedown is not the end of ransomware by any stretch. Groups like this often disappear, rebrand, or pop back up under a new name after a major hit. Even so, cutting off servers, seizing data, and exposing how the operation allegedly worked sends a loud message to the next crew thinking about following the same path.
