
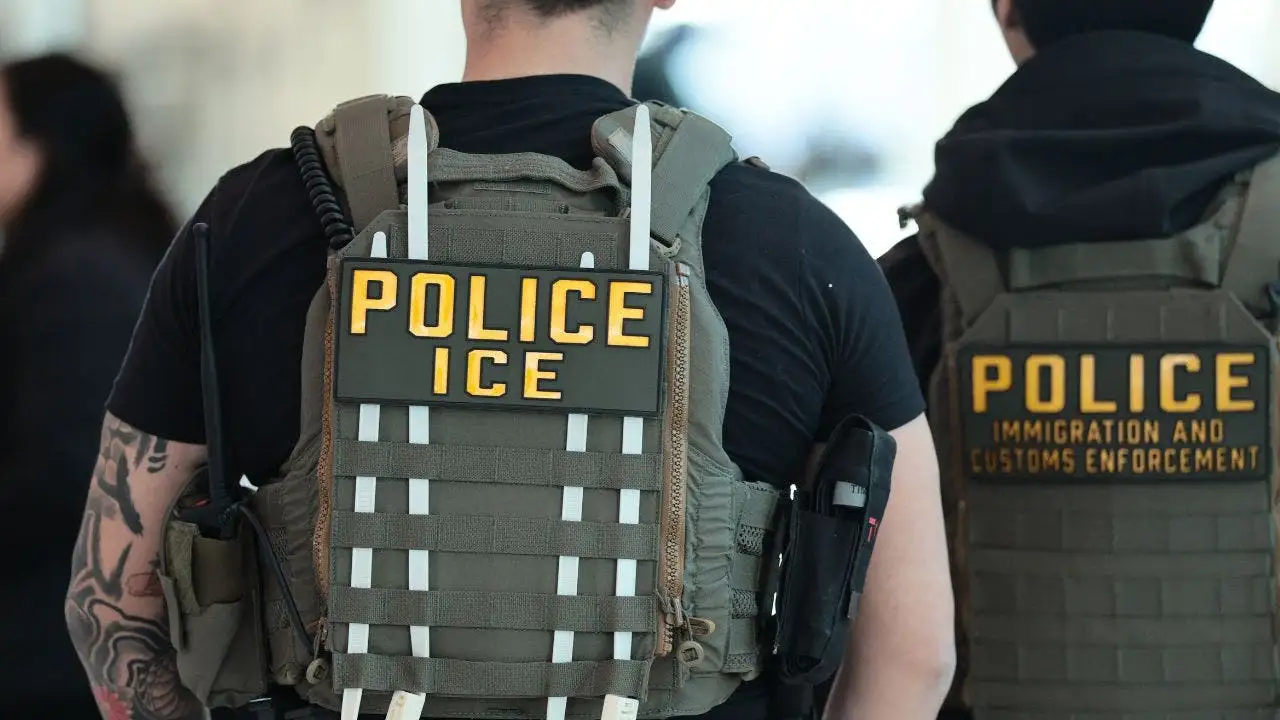
A massive Homeland Security data leak has put a spotlight on how fragile sensitive government records can be when the wrong people get access. The breach reportedly exposed contact details, office locations, internal group memberships and other personnel data tied to more than 41,000 employees and contractors, including ICE and Border Patrol workers. What makes this especially troubling is the possible exposure of undercover-related assignments and internal technology references that could help outsiders piece together how DHS operates.
According to the records, the leak centered on files published under the name Icepick and linked to a group calling itself the Department of Peace. The data reportedly spans DHS and several of its component agencies, with a heavy concentration of records tied to Customs and Border Protection and Immigration and Customs Enforcement. Even if the material does not appear to include home addresses or passwords, it still creates a real security problem when names, phone numbers, supervisors and access groups are all sitting in one searchable pile.
The biggest alarm bell comes from the overlap with undercover and surveillance-related activity. Researchers found internal groups that appear to reference certified undercover operations, communications interception and other sensitive programs. That does not automatically prove every listed person was actively undercover, but it does suggest enough about structure and assignments to create risk for ongoing investigations and the people involved in them.
Former acting ICE director John Sandweg called the exposure a “nightmare scenario”, and it is easy to see why. When sensitive personnel relationships become public, even partial details can help outsiders connect dots they were never supposed to see. In the world of law enforcement and national security, that kind of pattern recognition can be just as damaging as a direct leak of a case file.
The records also point to technology used inside DHS, including tools tied to investigative analysis and surveillance work. Mentions of Palantir, ChatGPT, Gemini, Copilot and even Grok showed up in the internal group names, which gives a glimpse into the digital tools connected to the department’s workflow. That does not mean the companies themselves were breached, but it does reveal what kinds of systems may be in play behind the scenes.
That detail matters because modern breaches are not just about stolen names anymore. They are about context, habits and internal access, the kind of information that helps an attacker understand who uses what, where systems sit and how people communicate. Once that map is exposed, the risk of phishing, impersonation and targeted intrusion jumps fast.
The reported entry point is still murky. The group claiming credit said it got access through DHS’s Okta sign-in system, but Okta says it has no evidence its own systems were compromised. DHS says it is investigating, and until that process is finished, the full path into the records remains unresolved.
That uncertainty is part of what makes the incident so frustrating. The public knows a breach happened, but not exactly how far it reached or who may have touched the data along the way. For now, officials are working with a narrow picture that confirms personnel records and access-group details were exposed, while leaving open the larger question of whether the incident went deeper than reported.
There are already signs that the leak has caused real-world fallout. Efforts to remove the data from hosting services reportedly ran into resistance, and the material appeared to keep resurfacing elsewhere online. Threats and hostile chatter followed in the wake of the release, which is exactly the kind of escalation that makes these leaks so dangerous once they are out in the open.
That part of the story should grab attention far beyond Washington. A federal employee list might sound like boring admin paperwork, but it can become a powerful weapon when paired with social media, public profiles and old data from other breaches. Someone with enough pieces can build a believable scam, fake a supervisor’s voice, or craft a message that looks far too real to ignore.
That is why workplace leaks are not just a government problem. They are a reminder that ordinary contact information can become a launchpad for targeted fraud, especially when criminals know where people work, who they report to and what systems they use. The more detailed the exposure, the easier it becomes to pressure, manipulate or intimidate someone.
For employees, the practical response is not panic, but caution. Unexpected password resets, urgent IT requests and messages that seem to know too much should always trigger suspicion. If a sender claims to be internal, verify it through a trusted channel, not by clicking the first link or replying in a hurry.
Strong account security also matters more when personal details are floating around in the wild. Unique passwords, multifactor authentication and a careful look at recovery settings can block a lot of opportunistic attacks before they get moving. It is the kind of boring protection that pays off in a hurry when someone tries to use stolen context against you.
There is also the broader privacy problem. Once personal data enters the ecosystem of brokers, people-search sites and reposted databases, it tends to spread instead of disappear. Cutting down what strangers can find online will not erase a government leak, but it can make follow-on harassment and impersonation a lot harder to pull off.
What stands out most here is how fast a supposedly internal record system can turn into a public safety issue. The mix of sensitive personnel names, internal access groups and technology references gives outsiders far more to work with than they should ever have. And as the records keep circulating, DHS is left trying to close a door that may already have been kicked wide open.
